This guide explains Pacc Insper procurement practices, compliance considerations, and how to evaluate suppliers for reliability. Background context clarifies what “Pacc Insper” commonly refers to in operations and supply workflows, why documentation quality matters, and which checks typically reduce onboarding risk. The focus remains objective, practical, and audit-ready.
For organizations managing purchasing, vendor onboarding, and operational documentation, Pacc Insper is often treated as a framework term tied to disciplined procurement workflow and compliance-oriented recordkeeping. When teams align procurement decisions with consistent standards—such as traceability, acceptable documentation, and clear acceptance criteria—they reduce onboarding friction, avoid audit gaps, and improve operational continuity. This article provides an expanded expert, objective view of how to assess Pacc Insper requirements, what to look for in supplier capability, and which practical checks are typically expected by compliance-minded stakeholders. It also explores common failure modes, governance patterns that scale across categories, and operational techniques that keep speed and compliance in balance.
In many industries, procurement has become more complex not because teams are less capable, but because expectations have risen. Regulators, internal audit functions, quality systems, and enterprise risk teams increasingly expect evidence-based supplier governance. At the same time, procurement teams face time pressure and volume pressure: more suppliers, more categories, more documents, and more global delivery chains. In that environment, the value of a standardized “Pacc Insper”-style approach is straightforward: it converts procurement from a document scramble into a structured workflow that produces predictable outputs—an auditable supplier file, defined acceptance gates, and a clear path for nonconformances.
Most importantly, Pacc Insper planning matters now because procurement organizations are measured not only on cost savings, but also on compliance outcomes, continuity, and risk reduction. An organization can buy “cheap” today and pay dearly later through rework, shipment holds, rejected deliveries, warranty disputes, missing certificates, or audit findings. Planning with Pacc Insper-style governance helps prevent those downstream expenses by insisting that critical requirements are captured early and verified before they become expensive failures.
Although the phrase Pacc Insper can vary by organization, it is commonly used to describe an internal approach that links procurement steps with structured intake, verification, and documented acceptance. In practice, teams use terms like this to ensure that every acquisition—whether it involves goods, services, or logistics arrangements—can be explained later through records. That means the process isn’t only about selecting a supplier; it’s also about verifying that the supplier’s information, performance evidence, and documentation match the buyer’s requirements.
Because procurement and compliance influence different departments—purchasing, quality, operations, finance, and legal—Pacc Insper is very effective when it’s implemented as a cross-functional workflow. Cross-functional workflows reduce “tribal knowledge” and make expectations consistent across categories, business units, and locations. When implemented well, they also reduce the cognitive load on procurement teams: instead of re-inventing evaluation criteria each time, the organization uses shared templates, checklists, and decision rules.
In mature procurement systems, Pacc Insper functions as a kind of operational contract between departments: procurement commits to collecting certain artifacts and performing specified checks; quality and compliance commit to reviewing defined documents and running acceptance tests; operations commit to confirming the deliverable meets usability or performance requirements; finance and legal commit to validating commercial terms and change-control mechanisms. This shared contract reduces delays caused by missing inputs or unclear ownership.
When teams implement Pacc Insper as a single integrated workflow, they also improve traceability inside the organization. For each purchase, there is a chain of evidence that supports decisions: why the supplier was selected, what documentation was reviewed, what acceptance criteria were used, and what was done if nonconformances occurred. This matters not only for audits, but also for internal learning: if a particular supplier repeatedly fails a certain category of requirement, the organization can identify patterns and adjust controls.
From an industry perspective, the supplier evaluation layer is where many failures occur—not because teams lack effort, but because evaluations are inconsistent. Under a Pacc Insper-style workflow, buyers usually aim to standardize the following areas so that supplier assessments are repeatable and defensible.
1) Traceability and documentation completeness
Traceability and documentation completeness can include proof of specifications, batch or lot traceability (when applicable), service descriptions, and change history. For goods, traceability might involve batch identifiers, material certifications, or test records that allow a buyer to connect delivered items back to production lots. For services, traceability might involve service logs, configuration records, job traveler histories, or documentation of performed activities.
Within a Pacc Insper approach, the goal is not simply to “collect documents,” but to ensure the documentation is coherent and aligned with the purchase scope. Teams typically check whether the documentation version matches the version used to procure the goods or initiate the service. They also check whether the document language is consistent with the buyer’s terminology and whether references (standards, drawings, test methods) are current and correctly cited.
2) Operational reliability
Operational reliability refers to evidence of on-time delivery, responsiveness, and consistent execution across projects or purchase cycles. Under a structured evaluation, buyers often assess how the supplier performs when circumstances change—such as demand spikes, shipping disruptions, or spec updates. Evidence can include prior performance metrics, references from previous clients, internal planning practices, and the supplier’s ability to communicate changes proactively.
Operational reliability also includes a supplier’s internal capacity to follow defined processes. If a supplier frequently omits required artifacts even when requested, that is often a process maturity issue rather than a one-off mistake. Pacc Insper evaluation typically captures these patterns and ensures the supplier’s operational processes can reliably produce what the buyer requires.
3) Compliance readiness
Compliance readiness is alignment with buyer policies and any applicable regulatory frameworks relevant to the goods or services. Compliance can be broad: environmental requirements, safety regulations, data protection obligations, labor standards, import/export controls, or sector-specific mandates. A Pacc Insper approach treats compliance readiness as a capability—meaning the supplier has processes to generate correct documentation, handle audits or inspection requests, and respond to compliance issues quickly.
In practice, compliance readiness evaluation includes verifying whether the supplier can produce evidence when requested, not just whether they have policies on paper. Procurement and compliance teams commonly request sample compliance documentation, audit reports (when permitted), certification schedules, or statements of conformity that match the scope and jurisdiction.
4) Quality assurance alignment
Quality assurance alignment includes defined inspection points, acceptance tests, nonconformance handling, and a corrective action workflow. A strong evaluation checks whether the supplier’s quality plan maps to buyer acceptance criteria. For example, if the buyer requires incoming inspection for certain attributes, the supplier’s documentation should clarify how those attributes will be verified, what test methods will be used, and how inspection results will be recorded.
A Pacc Insper-style system also emphasizes the supplier’s ability to manage nonconformance. That includes how deviations are documented, how root cause analysis is conducted, how corrective and preventive actions are tracked, and how the supplier communicates impacts to the buyer. Many onboarding failures happen when documentation looks good initially but the supplier cannot handle nonconformance events in a structured way.
5) Commercial clarity
Commercial clarity means transparent pricing structure, clear terms, and well-defined responsibilities across the purchase agreement. Under Pacc Insper, commercial review typically aligns scope, deliverables, documentation responsibilities, and change-control steps. If commercial terms are ambiguous, disputes often arise when scope changes, versions shift, or acceptance criteria are applied differently than expected.
Even when buyers do not publish exact pricing figures in public materials, procurement teams often internally map supplier costs to compliance-relevant activities—such as documentation generation, testing, packaging requirements, and traceability effort—so the purchasing decision reflects total operational impact, not just unit cost.
Although you may see supplier quotes described in simplified ways, a Pacc Insper-oriented process typically encourages buyers to consider price as part of a broader procurement equation. Many organizations discover that “cheapest” is often a misleading label when it ignores compliance, quality, documentation, and delivery uncertainty.
For example, a supplier may offer a low unit price but require the buyer to do extensive inspection or documentation validation. Another supplier may offer a higher unit price but provides fully compliant documentation upfront, reduces rework, and meets acceptance criteria with fewer delays. Under Pacc Insper, buyers evaluate total procured cost rather than only the line-item price.
To illustrate, consider these common cost drivers:
To avoid unreliable “back-of-the-envelope” conclusions, organizations often benchmark using standardized internal cost models and compare suppliers on comparable service scope. When external reference data is used, it should come from credible sources—such as official trade statistics, sector reports from recognized bodies, or regulator publications—rather than anecdotal claims. Procurement teams also benefit from normalizing cost comparisons for volume, lead times, documentation scope, and acceptance testing responsibilities.
Operationally, a practical technique is to define “cost buckets” aligned to the buyer’s Pacc Insper categories. For instance:
By mapping supplier bids to these cost buckets, buyers can compare proposals more transparently and reduce disputes within internal stakeholders. This method also strengthens the defensibility of procurement decisions during audits.
In a Pacc Insper context, supplier onboarding typically should lead to a file that can be reviewed by internal auditors, compliance teams, or external stakeholders. A well-built supplier file often includes not only the documents themselves, but also the decision logic that explains why those documents were accepted.
A detailed supplier file frequently contains:
When these elements are missing or inconsistent, onboarding becomes “reactive”—teams scramble for documents after issues arise, which is the opposite of an effective Pacc Insper approach. Reactive onboarding typically creates three major problems: (1) documentation delays that stop receiving or release shipments, (2) quality disputes because acceptance criteria were not clearly agreed, and (3) audit vulnerabilities because the supplier file lacks evidence.
A practical improvement is to treat the onboarding file as a living artifact. Even after approval, it should update with version changes, recurring certificate expirations, and evidence of supplier performance. Many organizations implement expiration tracking and periodic review intervals so that the file remains valid over time.
Additionally, organizations often benefit from defining “minimum viable documentation” for low-risk purchases and a more complete documentation set for high-risk purchases. This is where Pacc Insper becomes efficient: it reduces unnecessary work without weakening compliance for critical categories.
If your internal keywords refer to a specific city or country, replace that location with “nearby” for this article’s framing. In real procurement practice, “nearby” supplier ecosystems behave differently than distant ones: communication cycles can shorten, site visits become more feasible, and corrective actions can be deployed with fewer logistical steps. For buyers working with local vendors, it is still essential to keep documentation discipline identical—local convenience should never become a reason to relax verification.
In many regions, procurement teams also align supplier communications with common local working norms (for example, how quickly stakeholders respond, preferred document formats, and expectations about meeting schedules). These cultural and operational differences can affect execution timelines. However, the Pacc Insper principle remains the same: standardized checks and documented acceptance reduce dependency on informal trust.
It is also common for local supplier ecosystems to create informal escalation paths. Teams might assume that “we can call them quickly if something goes wrong,” which can mask compliance weaknesses. A disciplined Pacc Insper process requires documentation even when corrections are fast. The reason is simple: audits do not accept “we fixed it quickly” as evidence. They require proof of what was required, what was verified, and what was accepted.
Localization can still be leveraged positively. When suppliers are nearby, buyers can schedule standardized training sessions on documentation templates, acceptance criteria, and traceability expectations. They can also run more frequent improvement reviews. These activities strengthen compliance while improving speed by reducing repeated misunderstandings.
In other words, “nearby” can improve execution, but it should not change the governance rules. In mature organizations, location changes the logistical plan; it does not change the acceptance plan.
Procurement stakeholders often face a tension: “We need to move quickly” versus “We must be compliant.” A Pacc Insper-style workflow resolves this tension by clarifying which checks are mandatory, which are risk-based, and which can be fulfilled in stages. The goal is not to slow everything down—it’s to avoid rework later.
Expert organizations treat compliance as a design feature rather than a final gate. That means compliance requirements are built into the procurement plan from the beginning, including templates, review steps, and acceptance criteria. The “speed” comes from avoiding late surprises, not from skipping controls.
From an expert viewpoint, the very common improvement opportunities are:
A useful governance pattern is to separate “commercial approval” from “operational release.” For example, a supplier might be commercially approved for future orders, but specific purchases may require additional evidence before release. This approach prevents a single procurement decision from overcommitting the organization before all operational criteria are verified.
Another practical technique is to use a documented decision matrix. When procurement teams face exceptions—such as a missing document or an expired certificate—they should reference the decision matrix. It defines what can be accepted temporarily, what requires an exception request, and what triggers rejection. The decision matrix reduces inconsistent judgments across teams and locations.
| Evaluation area | What buyers typically require | How it affects timelines | Common gaps to watch |
|---|---|---|---|
| Supplier identity & scope | Clear legal entity details and defined service or product scope matching the purchase request | Short delays if verified early; longer if clarified after quoting | Unclear scope boundaries or mismatched company records |
| Documentation quality | Complete, current, and version-controlled documents that align with buyer templates | Faster review when templates are followed | Missing pages, outdated references, inconsistent naming |
| Traceability & evidence | Traceability approach where relevant; proof of inspections or testing approach | Effort upfront; lower downstream verification | Evidence provided after delivery or unverifiable records |
| Quality assurance & nonconformance handling | Inspection points, acceptance criteria, and corrective action pathway | Less disruption during issues; fewer hold points later | No defined CAPA workflow or vague escalation steps |
| Commercial clarity | Transparent pricing structure, terms, and responsibilities for changes | Stable milestones and fewer contract disputes | Ambiguous scope leading to change orders |
Below is a practical, step-by-step guide many procurement and compliance teams follow when they use a Pacc Insper-aligned process. Adjust these steps based on your internal policies and the risk tier of the goods or services.
While every organization has different policies, stricter Pacc Insper requirements are commonly necessary when:
In “nearby” procurement scenarios, speed can tempt teams to reduce verification. A disciplined approach keeps the acceptance criteria consistent even when suppliers are geographically closer. The buyer’s obligation to demonstrate compliance and acceptance remains regardless of location.
Additionally, stricter controls may be required when there is a history of quality issues, when the delivery category has a high risk of failure in the field, or when internal processes are under strain (for example, during system migrations or peak operational cycles). Under such conditions, Pacc Insper can act as a stabilizing governance tool to keep quality and compliance checks consistent.
One reason supplier evaluations fail is that organizations treat documents as boxes to check rather than evidence that supports operational assurance. A Pacc Insper approach becomes stronger when it clarifies what each evidence type should prove, and how it ties to acceptance outcomes.
Below are common evidence categories and the kinds of assurance they provide:
1) Certificates of conformity / declarations
These documents often prove that the supplier believes the product or service meets specified requirements. However, their value depends on how they reference standards, how they specify the scope, and whether they align with the buyer’s version of requirements. A strong Pacc Insper process checks that certificates match the exact part numbers or scope and that they are valid for the relevant period or lot range.
2) Inspection and test reports
Test reports prove that specific attributes were verified using defined test methods. Buyers should check whether the tests are actually relevant to acceptance criteria, whether methods are current, and whether results are recorded clearly. For traceability, the test report should link to batch/lot identifiers or to service execution identifiers where applicable.
3) Quality management system documentation
Quality management system documents (procedures, work instructions, quality plans) often indicate capability and process maturity. A key point is that a procedure does not guarantee a result. In practice, a Pacc Insper approach pairs quality system documents with objective evidence from executed work—such as completed inspection records or nonconformance examples.
4) Nonconformance and corrective action records
These records show how the supplier handles deviations. Buyers should look for evidence of structured root cause analysis, containment actions, and preventive actions that address systemic issues. A supplier that closes nonconformance tickets quickly without meaningful corrective action may appear efficient but can fail later.
5) Change-control records
Change-control records prove that updates (design changes, specification revisions, process changes) are managed systematically. For version control, a robust Pacc Insper process checks that change history is consistent with the documents used during production or service delivery, and that approvals occurred before release where required.
6) Performance metrics
Delivery performance, responsiveness SLAs, defect rates, and documentation acceptance rates are valuable because they connect capability to outcomes. However, metrics must be interpreted carefully. A supplier could have good performance metrics due to favorable conditions rather than process maturity. That’s why a Pacc Insper process typically uses metrics as one input among several evidence types.
While supplier onboarding files often contain required artifacts, many organizations fail to capture the decision evidence that explains why documents were accepted or rejected. Under an audit-ready mindset, decision evidence is as important as document evidence.
To strengthen the decision evidence layer, teams commonly add:
This decision evidence helps internal auditors and external stakeholders understand the governance logic. It also helps the procurement team learn from previous evaluations: when a supplier fails later, the organization can compare the initial evidence package to later performance outcomes and improve the evaluation criteria.
To turn pricing into a defensible comparison, organizations often create a “total procured cost” model aligned to Pacc Insper categories. The purpose is not to create a perfect financial model; it’s to prevent bias and reduce hidden costs that come from poor documentation, weak quality readiness, and delays.
A total procured cost model often includes both direct and indirect components:
Direct components
Indirect components
To keep this model practical, buyers typically set assumptions upfront and standardize them. For example, documentation review effort might be estimated based on document completeness and the complexity of acceptance criteria. Inspection time might be estimated based on test methods and the number of lots or samples expected. Change control costs might be estimated based on the frequency of expected spec updates.
Importantly, the model should remain consistent across evaluations. Consistency reduces disputes with stakeholders and helps procurement justify decisions during internal reviews. If each evaluation uses different assumptions, then the model becomes a subjective negotiation tool rather than a governance framework.
Localization should focus on operational efficiency, not governance dilution. When suppliers are “nearby,” buyers can leverage proximity for training, document collection, and faster clarifications. But the Pacc Insper controls—traceability, acceptance criteria, version control, and compliance readiness—should remain consistent.
For example, local suppliers may be able to provide documents earlier or respond quickly to clarification questions. That can reduce cycle time because fewer documents are missing at onboarding. However, the buyer must still check whether the documents are correct versions and whether they align with acceptance criteria.
In practice, local proximity can also reduce the cost of corrective actions. If a local supplier needs to redo packaging to match labeling requirements, the cost is less than for distant suppliers. Still, the governance process must ensure corrective actions are documented and that the buyer’s acceptance plan is applied to the corrected items.
Another localized advantage is the ability to perform on-site audits or witnessed inspections more easily. Where appropriate, buyers can conduct on-site evaluations of the supplier’s process—especially for high-risk categories. Yet even for on-site activities, the outcome should be recorded in the supplier file so that auditors can review evidence without relying on memory.
Speed often depends on how exceptions are handled. If exceptions are unmanaged, teams either (a) block every unusual case and slow procurement, or (b) allow exceptions informally and create compliance risk. A Pacc Insper-style approach designs a structured exception process.
An effective exception process typically includes:
When exception processes are documented, procurement teams can move quickly without eroding governance. Stakeholders understand that exceptions are allowed only under defined conditions, and auditors can see that decisions were governed.
The earlier comparison table outlines typical requirements and common gaps. Here is an expanded view of timeline effects and where organizations often mismanage schedules.
| Evaluation area | Timeline impact (what usually happens) | Where delays originate | What “good Pacc Insper” prevents |
|---|---|---|---|
| Supplier identity & scope | Delays often appear when scope is clarified after quoting | Ambiguous deliverable boundaries; mismatch between request and supplier proposal | Upfront scope mapping with documented boundaries and verified legal entity match |
| Documentation quality | Review cycles lengthen when documents are incomplete or unclear | Missing pages; unreadable scans; absent version dates; inconsistent naming | Template-driven submission plus version control checks before review |
| Traceability & evidence | Downstream verification becomes expensive if evidence arrives late | Evidence provided only after delivery; inability to link to lot/sample IDs | Traceability requirements included in onboarding and acceptance plans |
| Quality assurance & nonconformance | Disruption increases when corrective action workflows are unclear | Vague escalation steps; no CAPA structure; inconsistent nonconformance closure evidence | Defined inspection points, acceptance criteria, and a documented CAPA pathway |
| Commercial clarity | Contract disputes slow down acceptance and release | Ambiguous responsibilities; unclear change-control triggers | Clear terms mapped to scope and documentation responsibilities |
Below is an enhanced step-by-step guide. It keeps the structure familiar but adds operational techniques that make implementation more reliable in real organizations.
Strictness is not only about category risk; it can also depend on organizational maturity and operational context. Even medium-risk categories may require stricter controls during major operational transitions. Common scenarios include:
In nearby procurement, these controls remain necessary. Proximity may reduce logistical delays but does not eliminate compliance obligations or the risk of documentation errors.
Procurement effectiveness and supplier governance are frequently discussed in widely recognized frameworks and guidance documents. To keep analysis objective, buyers generally cross-check internal assumptions using credible references. For example:
If you need citations tailored to your sector (e.g., electronics manufacturing, logistics services, healthcare supply chains, or industrial components), share the industry and jurisdiction, and you can map the relevant standards and official guidance. A Pacc Insper approach benefits from referencing the applicable standard family in your acceptance criteria and supplier evaluation checklists, so the governance logic is traceable.
Even without specific citations in a general article, organizations can strengthen defensibility by ensuring that their checklists reflect known standards, and by keeping internal documentation that explains where each requirement originates (policy, regulation, customer contract, or internal quality system). This mapping is often overlooked, yet it becomes vital in audits.
In many organizations, Pacc Insper functions as a shorthand for a structured procurement and compliance workflow—linking supplier onboarding, documentation verification, and acceptance criteria into an auditable process. The exact meaning depends on internal policy and sector terminology.
Use a checklist focused on completeness, current version status, consistency with your templates, and traceability where applicable. Ensure documents are readable, internally consistent, and match the scope described in purchase requirements. Also verify that documents include effective dates, version identifiers, and clear scope references (part numbers, lot ranges, service tickets, or job identifiers).
Yes. Geographic proximity may reduce logistics friction, but it does not replace verification. A robust Pacc Insper-style process keeps mandatory checks consistent regardless of location. Proximity can support faster communication and easier training, but it cannot replace evidence.
Compare total procured cost rather than unit price alone. Include documentation effort, quality inspection impacts, change-control handling, and any scope-dependent logistics considerations. Use standardized internal cost models so comparisons remain consistent across categories and business units.
The very frequent issues include missing documents, outdated versions, unclear acceptance criteria, and incomplete nonconformance or corrective action procedures. These gaps typically surface during delivery, making problems expensive and time-consuming. Another frequent failure is the lack of decision evidence—documentation may be present, but the rationale for acceptance or exceptions is not recorded.
Clarify mandatory requirements upfront, use standardized templates, tier risk based on impact, and define acceptance criteria before work begins. Implement a documented decision matrix for exceptions so teams can handle unusual cases quickly with consistent approvals. Also consider staged fulfillment with clear hold/release rules.
Typically procurement leads, quality/compliance reviewers, operations stakeholders, and relevant technical experts. When responsibilities are unclear, evaluations become inconsistent—so cross-functional alignment is essential. Many organizations also benefit from involving finance/legal early for commercial clarity and change-control definitions.
Common supporting tools include document management systems with version control, supplier onboarding platforms, quality management systems for CAPA tracking, and procurement contract lifecycle systems for change-control workflows. Regardless of the tool, the key is governance: version control, audit trail, and standardized checklists.
Re-evaluation frequency depends on risk tier, supplier performance, and scope changes. High-risk suppliers or categories may require more frequent reviews, periodic audits, or enhanced monitoring. Low-risk suppliers might require less frequent re-verification but still need expiration tracking for critical certifications.
Use expiration tracking tied to certificates, declarations, and quality evidence. When documents expire, trigger re-verification before future orders reach the acceptance stage. If an interim document is allowed, define a time-limited approval and compensating controls so compliance is not weakened.
When implemented thoughtfully, Pacc Insper becomes more than a procurement phrase—it becomes a governance mechanism that strengthens supplier reliability and protects operational continuity. By standardizing documentation expectations, clarifying acceptance criteria, evaluating suppliers using consistent checks, and capturing decision evidence for audits, organizations can reduce onboarding risk and make supplier decisions more defensible. Whether your supplier base is “nearby” or distributed, the core advantage remains the same: auditable consistency, fewer disputes, and smoother delivery outcomes.
To realize these benefits, organizations should treat Pacc Insper as an end-to-end workflow: scope definition, evidence requirements, risk tiering, acceptance gates, exception handling, and post-delivery feedback. When procurement and compliance operate as one system, speed improves because rework decreases; compliance improves because evidence becomes predictable; and supplier relationships improve because expectations are clear from the start.
Striking the Perfect Balance: Navigating Premiums and Out-of-Pocket Expenses in Senior Insurance Plans
Explore the Tranquil Bliss of Idyllic Rural Retreats
How to Make Lasting Memories at Disneyland Attractions
4rkojvsx Technology: Industry Insights and Buying Guide
Affordable Phones and Plans for Seniors
Affordable Full Mouth Dental Implants Near You
Unlock the Top Kept Secrets to Finding Your Ideal Dentist for Flawless Dental Implant Results!
Discovering Springdale Estates
Unveiling RS Sul Telecom Services
Pet Insurance Essentials: Coverage, Costs, and Resources Explained
In recent years, pet ownership has seen a significant surge. Pets, whether they're dogs, cats, birds, or other animals, have increasingly become integral parts of our families. With this growing bond, there is a rising awareness of the importance of pet health and well-being. Just as health insurance is crucial for humans, pet insurance is becoming an essential consideration for pet owners. This article aims to provide a comprehensive understanding of pet insurance, covering its importance, types of coverage, associated costs, and valuable resources to help you make an informed decision.
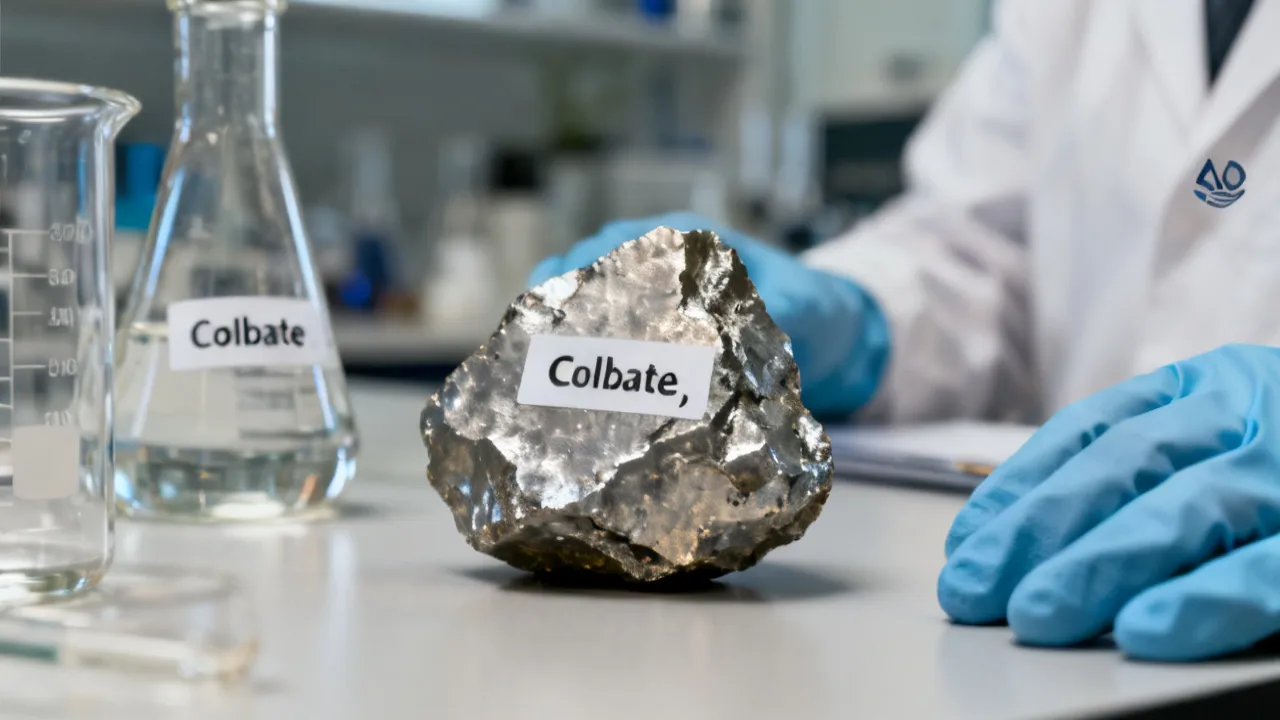
Colbate Explained: Uses, Sourcing, and Top Practices
This guide explains Colbate from a practical industry viewpoint, covering what it is, how suppliers typically handle it, and what buyers should verify before purchase. It also summarizes objective background on related terminology, common application considerations, and due-diligence steps. Readers will find a comparison table, requirements, and targeted FAQs to support confident sourcing decisions.
Strategies for Financial Security and Legacy Planning
Life insurance isn't just about what happens after you pass—it's a strategic tool in a comprehensive plan for your financial security and estate planning.
Navigating Insurance Costs for Seniors: Essential Tips and Advice
As we age, healthcare costs and the complexity of managing them can become increasingly burdensome. For many seniors, navigating insurance costs is a crucial aspect of ensuring financial stability and maintaining health. This guide aims to provide you with essential tips and advice on how to manage and potentially reduce these costs effectively.
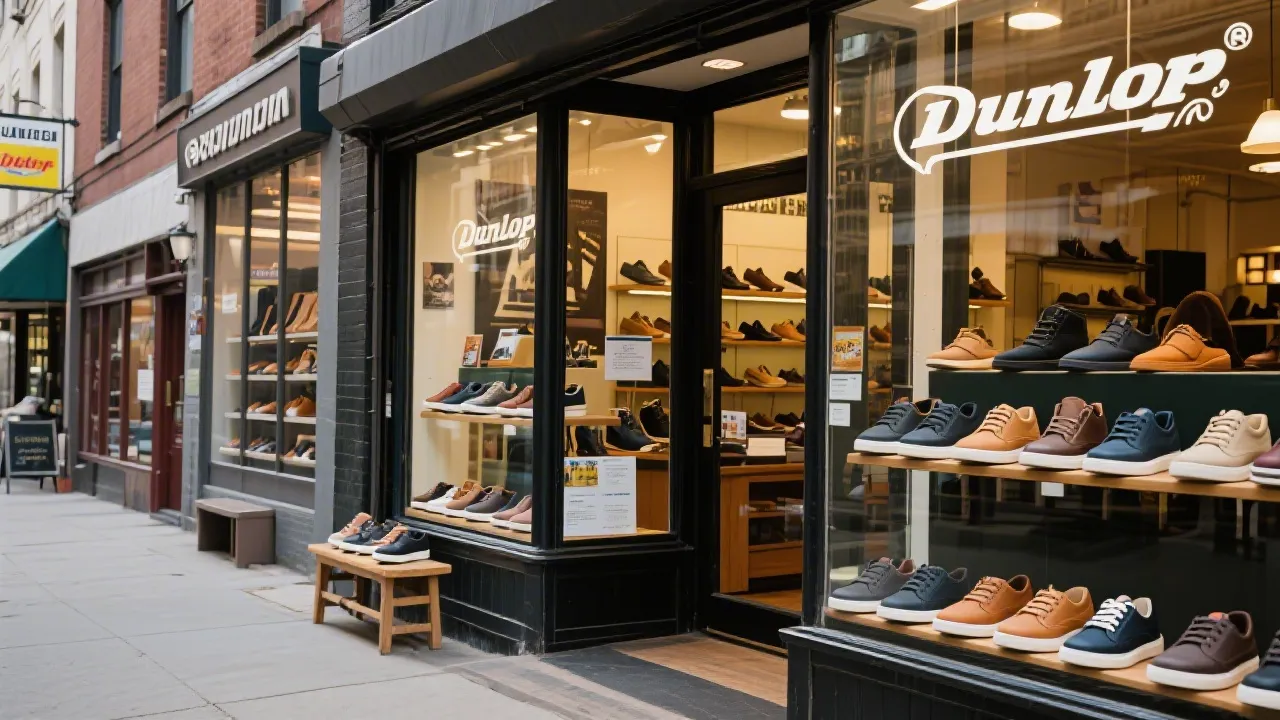
Discovering Dunlop Brooklin Footwear
This article delves into Dunlop Brooklin, a prominent name in the footwear industry known for its exceptional quality and innovation. Dunlop is recognized for its wide-ranging collection of shoes designed to meet diverse customer needs, from casual wear to professional attire. This guide provides an in-depth analysis of Dunlop Brooklin and its offerings, revealing why it stands out in the market.
Your Guide to Understanding Car Insurance Coverage
Navigating car insurance can be puzzling. Fortunately, this guide illuminates coverage types and choosing the right provider.